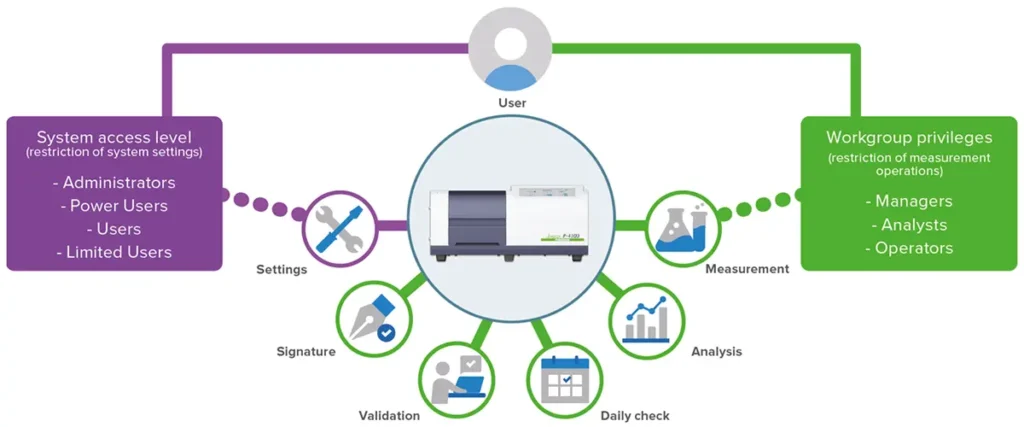
Based on the dual security structure ([Access Level] and [Work Group]), it is possible to manage different authorization process in flexible and independent as total analysis systems, instrumentations and analytical applications.
Based on prohibiting function to delete electronic record and to overwrite save, and also functions for automatic backup and restore data, electronic records can be saved properly and can be searched accurately during the data lifecycle.
It is categorized as 3 different records (system log, application log and data log), and it is recorded.
Each log can be filtered and displayed under recorded date, user name etc, and it can be exported to audit trail review as text file.
Based on functions to prevent duplicate account or to protect password, and to prevent unauthorized access, administrative authorizations as system access and electric signature etc., can be managed strictly.